Classical public-key infrastructure (RSA & ECC) is cryptographically broken against Shor's algorithm. RedLens Enterprise 3.7 delivers post-quantum ephemeral lattice key encapsulation (NIST FIPS 203 ML-KEM-768, p50=1.33ms), RFC 9106 Argon2id + AES-256-GCM zero-cleartext encryption, active bit-flip tamper rejection, and a turnkey Docker sidecar API for cloud & autonomous AI agent workloads.
State-sponsored actors and institutional adversaries intercept and store encrypted internet traffic today, awaiting cryptanalytically relevant quantum computers (CRQCs) to shatter RSA and Elliptic Curve Diffie-Hellman via Shor's algorithm.
Every session cookie, Bearer JWT, and private API secret routed through standard TLS (RSA-2048 / ECDHE-P256) is mathematically obsolete. Quantum polynomial factoring will retroactively expose recorded archives.
Naive post-quantum implementations fail against Chosen-Ciphertext Attacks (IND-CCA2). Malicious intermediaries flip single bits on the wire to extract private key coefficients through decryption error oracles.
Traditional enterprise VPNs and proxies install invasive Ring-0 kernel drivers (`.sys`), exposing workstations to blue screens, anti-cheat bans, and privilege escalation vulnerabilities.
Rooted in the Module-Learning with Errors (M-LWE) problem over the cyclotomic polynomial ring Rq = ℤq[X] / (X256 + 1).
RedLens applies the Fujisaki-Okamoto (FO) transform. When an adversary injects bit-flip tampering onto the wire, the internal re-encryption validation check triggers an active rejection failure:
[PQC-AIRLOCK] ⚠️ Active Bit-Flip Detected!Calculated c' ≠ Received c ➔ Decapsulation Terminated.Zero Plaintext Leakage. Session Sealed.
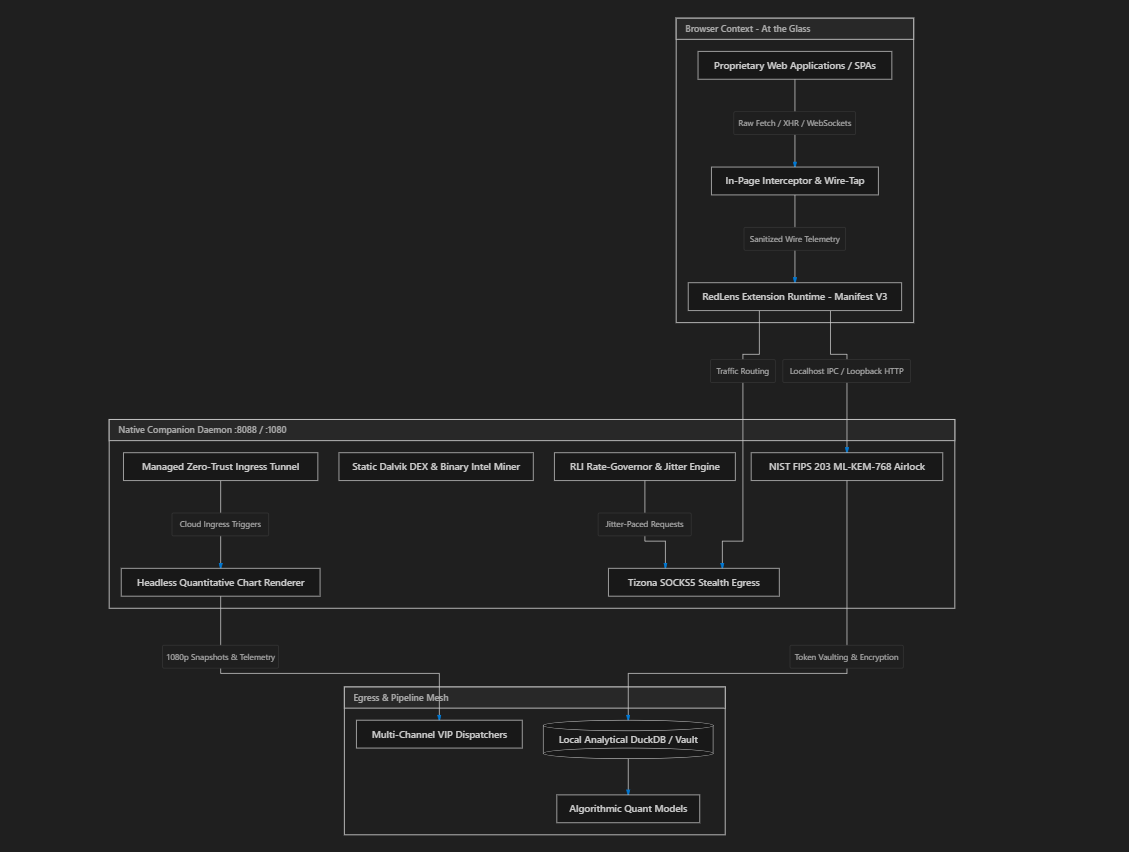
From in-page JavaScript interception to user-space SOCKS5 multiplexing and DuckDB analytical storage.
Ratified on Windows 11 x64 (AMD64, Python 3.12.10) with direct native C-bindings to liboqs and Windows DPAPI hardware sealing. All 6 empirical claims verified with zero simulated mock fallbacks.
e28179cdea79f8677590bb3459f5e28daf2b72c7e993fb3c0f319f1351c1bcf811b938ed7ac55924bd962e10e1f4c9f76c072756b4dc58a9bbf0f08f53554c5c
python tests/commercial_verification_suite.py
100 consecutive encapsulation/decapsulation cycles with C-compiled liboqs backend.
64MiB RFC 9106 KDF + active adversarial bit-flip corruption across payload, nonce, and GCM tag.
Windows CryptProtectData hardware key encryption with auto-detecting Linux Docker container mode.
25 high-entropy cloud credentials sealed; raw byte scan executed across entire on-disk vault files.
High-throughput columnar ingestion and aggregation over PQC-AEAD encrypted API telemetry rows.
Standardized HTTP sidecar with Bearer token authentication, secret leasing, and tamper detection.
curl -X POST http://127.0.0.1:8088/v1/vault/lease \ -H "Authorization: Bearer redlens_enterprise_token_xxx" \ -H "Content-Type: application/json" \ -d '{"lease_id":"lease_9f1a","pqc_envelope":"...TAMPERED_1BIT_BYTE_542..."}'
Deploy RedLens Enterprise as a high-speed local container sidecar next to your AI agents, ECS tasks, Cloud Run services, or Kubernetes pods.
Runs seamlessly on AWS ECS, GCP Cloud Run, or Azure Container Apps with zero host kernel dependencies.
Fully compatible with OpenAI Swarms, Claude Code, AutoGen, and Antigravity Agent tools via OpenAPI 3.1.